The Binance Hack: Lessons for Financial Institutions and the Financial Centers Where They Operate
- 24 de novembro de 2026 · 25 de novembro de 20262 sessions for different time zones
- Live online webinar90 minutes
Thank you. Stripe sends you a receipt by e-mail, and the World Alliance sends you the link to the webinar before your session.
The payment was cancelled. You can try again below.
About the workshop
AI has changed both sides of the cybersecurity equation. It gives attackers cheap, convincing deception – false identities, tailored investment approaches, personalised lures – and it gives them something new to aim at, because the AI tools organisations now rely on hold access, read sensitive material and act on instructions.
Two incidents show what that looks like in practice. The Binance attack ran through compromised machines and the misuse of an internal AI tool to reach the wallet signing system. It shows why responding to such an incident means removing every remaining foothold, not just the first one. The Bybit attack shows how transaction details presented to a human approver can be made to mislead, defeating the control precisely because the approver did what the process asked.
This session will address the controls for financial centers. It will also cover AI used to write software, where unsafe changes, harmful packages and unauthorised releases can reach live systems. It covers AI in daily operations – what a tool may read, what it may act on, restricted permissions, payment limits, monitoring and how to stop unwanted activity. Additionally, it will cover AI suppliers and third parties: what is shared with providers, what must be re-checked when services or permissions change, and how essential work continues when a shared supplier is attacked.
The session will conclude with responsibilities of organisations, financial center networks and regulators with practical next steps including a short survey of entities under management, evidence checks and joint response exercises.
Participants will also receive a written guide covering the session’s topics and an AI review checklist.
Programme
- 8 minIntroduction: AI use, attacks and scams
- 18 minThe Binance case study
- 10 minBybit, and lessons from both incidents
- 10 minAI in software development
- 12 minAI in day-to-day operations
- 12 minAI suppliers and third parties
- 10 minResponsibilities and practical next steps
- 10 minQuestions, materials and references
Trainer
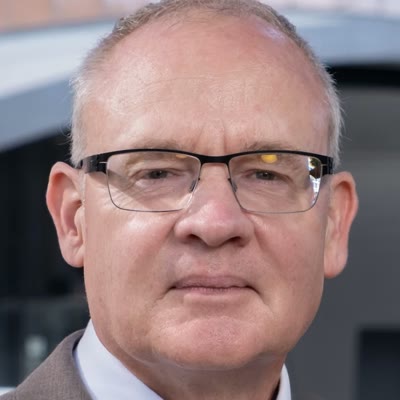
Marc Krisjanous is the founder and Principal Consultant of Zanarc Limited, an independent cybersecurity consultancy specialising in blockchain and digital asset security. With over 18 years of experience across information technology, information security and cybersecurity auditing, Marc specialises in cybersecurity assurance for blockchain and distributed ledger technology (DLT) systems and audits against internationally recognised security standards and frameworks. He also advises and trains central banks and financial regulators on the supervision of virtual asset service providers (VASPs). His professional interests include the emerging risks artificial intelligence poses to blockchain-based systems and decentralised systems, including AI-enabled attack vectors, the security implications of integrating AI agents within blockchain ecosystems and the development of control frameworks to address these threats.